Chris Jones Chris Jones
0 Course • 0 StudentBiography
Palo Alto Networks XSIAM-Engineer Exam Outline & Valid XSIAM-Engineer Test Duration
BTW, DOWNLOAD part of ActualTestsIT XSIAM-Engineer dumps from Cloud Storage: https://drive.google.com/open?id=1QqheTC7pUgDn6Cy5FD0Zm_HQM8ux4JyB
In order to facilitate the wide variety of users' needs the XSIAM-Engineer study guide have developed three models with the highest application rate in the present - PDF, software and online. Online mode of another name is App of study materials, it is developed on the basis of a web browser, as long as the user terminals on the browser, can realize the application which has applied by the XSIAM-Engineer simulating materials of this learning model, users only need to open the App link, you can quickly open the learning content in real time in the ways of the XSIAM-Engineer study materials.
Palo Alto Networks XSIAM-Engineer Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
>> Palo Alto Networks XSIAM-Engineer Exam Outline <<
100% Pass Palo Alto Networks - XSIAM-Engineer –Valid Exam Outline
The ActualTestsIT is one of the top-rated and renowned platforms that has been offering real and valid Palo Alto Networks XSIAM Engineer (XSIAM-Engineer) exam practice test questions for many years. During this long time period countless Palo Alto Networks XSIAM Engineer (XSIAM-Engineer) exam candidates have passed their dream XSIAM-Engineer certification and they are now certified Palo Alto Networks professionals and pursuing a rewarding career in the market.
Palo Alto Networks XSIAM Engineer Sample Questions (Q13-Q18):
NEW QUESTION # 13
An XSOAR integration for a custom internal security tool is generating malformed incident fields in XSIAM. Specifically, a field which should be a JSON object is appearing as a string representation of a Python dictionary (e.g., "{'browser': 'Chrome', 'os': 'Windows'}"). The XSOAR script uses before sending the dat a. What is the most likely cause for this behavior and how should it be corrected?
- A. There's an implicit type conversion happening during the data transfer from XSOAR to XSIAM, requiring explicit casting in the script.
- B. The data being passed to 'json.dumps()' is already a string, causing it to be double-encoded.
- C. The XSIAM incident field is configured as a 'String' type instead of a 'JSON' or 'Object' type.
- D. The XSOAR integration is not properly handling the *Content-Type' header when sending data to XSIAM, causing XSIAM to interpret it as a plain string.
- E. The 'json.dumps()' function is not being called correctly; ensure the Python dictionary is passed as an argument.
Answer: C
Explanation:
If is correctly called (meaning the Python dictionary is converted to a JSON string ), but XSIAM interprets it as a literal string (showing quotes around the entire JSON string or displaying it like a Python dictionary string representation), it strongly indicates that the target field in XSIAM is configured to accept a string, not a JSON object. XSIAM expects JSON objects for certain field types and will automatically parse them if the field type is correctly set. If it's a 'String' type, it will store the JSON string as a string
NEW QUESTION # 14
A Cortex XSIAM engineer is implementing role-based access control (RBAC) and scope-based access control (SBAC) for users accessing the Cortex XSIAM tenant with the following requirements:
Users managing machines in Europe should be able to manage and control all endpoints and installations, create profiles and policies, view alerts, and initiate Live Terminal, but only for endpoints in the Europe region.
Users managing machines in Europe should not be able to create, modify, or delete new or existing user roles.
The Europe region endpoints are identified by both of the following:
Endpoint Tag = "Europe-Servers" and Endpoint Group = "Europe" for servers in Europe Endpoint Group = "Europe" and Endpoint Tag = "Europe-Workstation" for workstations in Europe Which two sets of implementation actions should the engineer take? (Choose two.)
- A. Use the pre-defined roles, assign the "Privileged IT Admin" role to the user or user group managing Europe-based endpoints.
- B. Verify and confirm that SBAC mode under "Server Settings" is set to "Permissive," and assign "EG:
Europe" under the user permission scope configuration. - C. Verify and confirm that SBAC mode under "Server Settings" is set to "Restrictive," and assign "EG:
Europe" under the user permission scope configuration. - D. Use the pre-defined roles, assign the "Instance Administrator" role to the user or user group managing Europe-based endpoints.
Answer: A,C
Explanation:
To meet the requirements, the engineer must enable scope enforcement by setting SBAC mode to Restrictive and assigning the Europe endpoint group (EG:Europe) as the scope. For role assignment, the correct predefined role is Privileged IT Admin, since it allows endpoint management, policy creation, and Live Terminal but does not permit user role management.
NEW QUESTION # 15
A company is evaluating the security posture of its existing CI/CD pipelines and DevOps practices to align with XSIAM's DevSecOps principles. They use Jenkins for CI/CD, Gitlab for source code management, and deploy to Kubernetes clusters. What specific telemetry sources from this ecosystem are crucial for XSIAM, and how can XSIAM contribute to improving their 'shift-left' security posture?
- A. Crucial Telemetry: CPU and memory utilization metrics from Jenkins agents. XSIAM Contribution: Optimizes resource allocation for CI/CD pipelines based on security posture.
- B. Crucial Telemetry: Git commit logs, Jenkins build logs (including static application security testing (SAST) and dynamic application security testing (DAST) results), container image scan results from registries, Kubernetes audit logs. XSIAM Contribution: Consolidates these diverse logs for correlation, anomaly detection (e.g., unauthorized changes to CI/CD configs), and can trigger automated responses based on detected risks early in the pipeline.
- C. Crucial Telemetry: Network flow logs from Kubernetes pods. XSIAM Contribution: Monitors network traffic for anomalies within the build environment.
- D. Crucial Telemetry: User login activity to Jenkins. XSIAM Contribution: Provides basic user authentication logs from Jenkins.
- E. Crucial Telemetry: Only security scans from Jenkins. XSIAM Contribution: Provides a dashboard for vulnerability scan results from Jenkins.
Answer: B
Explanation:
To achieve effective 'shift-left' security with XSIAM, comprehensive telemetry from the entire CI/CD pipeline is necessary. This includes source code changes (Git logs), build and test results (Jenkins logs, including SAST/DAST), artifact integrity (container registry scans), and runtime security (Kubernetes audit logs, runtime protection for containers via Cortex XDR). XSIAM's strength lies in its ability to ingest, correlate, and analyze this disparate data, identifying threats, misconfigurations, or policy violations earlier in the development lifecycle, thereby 'shifting security left.' It provides consolidated visibility and the ability to automate responses based on these insights.
NEW QUESTION # 16
A global enterprise has implemented Palo Alto Networks XSIAM for its security operations. They are concerned about lateral movement within their Kubernetes clusters and want to establish an ASM rule to detect 'Pod Escapes' or suspicious activities indicative of a container compromise leading to host-level access. Assume XSIAM ingests container runtime events and host-level process data'. Which combination of XQL data sources and logic would be most effective for this complex detection?
- A.
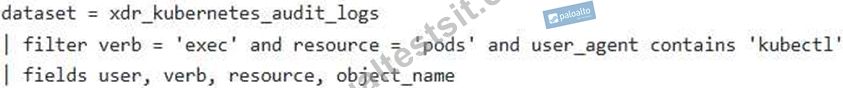
- B.

- C.

- D.

- E.

Answer: E
Explanation:
Option B is the most effective for detecting 'Pod Escapes' or container-to-host compromise. It directly looks for suspicious commands often used in container escapes ('nsenter', 'docker' commands like 'chroot' or 'mount /dev') in 'xdr_process_eventS at the host level. The 'inner join' with filtering for 'container_privileged = true' ensures that this suspicious activity is correlated with potentially vulnerable privileged containers, providing strong evidence of a potential escape. Option A is too generic network-wise. Option C is a general host compromise indicator, not specific to container escape. Option D is valid Kubernetes audit, but 'kubectl exec' into a pod isn't a pod escape itself. Option E is a specific example of an attacker action after escape, but Option B covers the escape mechanism more broadly and correlates with privileged containers.
NEW QUESTION # 17
An XSIAM Security Engineer is troubleshooting why certain high-severity alerts, triggered by a custom detection rule, are not consistently enriching with specific asset metadata (e.g., 'asset_owner', 'business_unit') from an external CMDB. The CMDB data is available as a daily CSV export on an SFTP server, and is ingested into a separate Data Lake dataset. The custom detection rule relies on a lookup from the CMDB dataset. The issue appears intermittent. Which factors are most likely contributing to this problem, and what content optimization strategy in XSIAM would be most effective to ensure consistent enrichment?
- A. The CMDB CSV export has inconsistent column headers or data types, causing the XSIAM Data Flow for CMDB ingestion to fail partially or misinterpret fields, leading to incomplete dataset population for lookups.
- B. The SFTP server connection for the CMDB export is intermittently failing, preventing the CMDB dataset from being updated regularly in XSIAM.
- C. The volume of security alerts is too high for the CMDB lookup to process in real-time within the detection rule, leading to dropped enrichments.
- D. The primary key used for the lookup (e.g., 'asset_ip') in the security alert data does not always exactly match the format or casing of the corresponding key in the CMDB dataset, causing lookup failures.
- E. The lookup table created from the CMDB dataset is not configured as a 'Live Lookup', meaning it's only updated periodically, leading to stale asset information for newly observed events.
Answer: A,B,D,E
Explanation:
This is a multiple-response question. All listed options (A, B, C, E) are highly plausible and common reasons for inconsistent lookup enrichment in XSIAM: A: Inconsistent CMDB CSV export: If the source CSV's structure or data types are not stable, the CMDB ingestion Data Flow might partially fail, resulting in an incomplete or corrupted lookup dataset. This directly impacts lookup accuracy. B: Lookup table not 'Live Lookup': For real-time enrichment of active security events, the lookup table derived from CMDB data must be configured as a Live Lookup. If it's a static lookup, it won't reflect recent CMDB updates, leading to stale or missing enrichments for new assets or changes. C: Mismatched Lookup Keys: This is a very common issue. Even minor discrepancies (e.g., '192.168.1.1' vs. '192.168.001.001', or 'hostname' vs. 'HostName') will cause lookup failures. Content optimization here involves ensuring both the CMDB ingestion Data Flow and the security event Data Flow normalize the lookup key format (e.g., to lowercase, remove leading zeros, consistent IP format) before the lookup. E: Intermittent SFTP failure: If the source data for the CMDB dataset (the CSV export) is not reliably ingested due to connectivity issues, the CMDB dataset in XSIAM will become outdated or incomplete, leading to lookup failures. Option D is less likely for lookup performance itself, as XSIAM's lookup capabilities are highly optimized. High volume might impact rule processing overall, but not specifically the lookup mechanism unless the lookup dataset itself is astronomically large and unindexed, which is generally not the case for CMDB data.
NEW QUESTION # 18
......
We are the fastest to pursue acquiring XSIAM-Engineer certification; we are the highest to pursue protecting your benefits. Our ActualTestsIT ensures the accuracy and the most coverage of XSIAM-Engineer Certification Exam Dumps. If you purchase XSIAM-Engineer certification exam dumps, we will ensure that you can get free update service in one year.
Valid XSIAM-Engineer Test Duration: https://www.actualtestsit.com/Palo-Alto-Networks/XSIAM-Engineer-exam-prep-dumps.html
- Exam XSIAM-Engineer Tips 🌑 XSIAM-Engineer Reliable Exam Online 🖐 XSIAM-Engineer Braindumps 👔 Search for ➥ XSIAM-Engineer 🡄 and download it for free immediately on ➠ www.troytecdumps.com 🠰 🐇XSIAM-Engineer Hot Spot Questions
- Valid XSIAM-Engineer Exam Outline - Leader in Qualification Exams - Fantastic Palo Alto Networks Palo Alto Networks XSIAM Engineer 🤗 Copy URL “ www.pdfvce.com ” open and search for [ XSIAM-Engineer ] to download for free 🌈New XSIAM-Engineer Test Format
- Test XSIAM-Engineer Dumps Pdf 🤛 XSIAM-Engineer Reliable Exam Online ⌨ Valid XSIAM-Engineer Exam Review 🦩 Search for ➽ XSIAM-Engineer 🢪 and download exam materials for free through ➤ www.prepawayete.com ⮘ 🚆Test XSIAM-Engineer Dumps Pdf
- Latest XSIAM-Engineer Test Materials 🎍 Valid XSIAM-Engineer Exam Online 🐤 New XSIAM-Engineer Test Format 💹 Simply search for ➠ XSIAM-Engineer 🠰 for free download on ⇛ www.pdfvce.com ⇚ ⤴XSIAM-Engineer Latest Test Report
- The Best XSIAM-Engineer Exam Outline offer you accurate Valid Test Duration | Palo Alto Networks Palo Alto Networks XSIAM Engineer 🩱 Search for 「 XSIAM-Engineer 」 and download it for free immediately on ▛ www.vce4dumps.com ▟ 💰Valid XSIAM-Engineer Exam Review
- XSIAM-Engineer Reliable Exam Online 🦕 Valid XSIAM-Engineer Test Book ▛ Test XSIAM-Engineer Dumps Pdf 🏥 Search on 《 www.pdfvce.com 》 for ✔ XSIAM-Engineer ️✔️ to obtain exam materials for free download 🔽XSIAM-Engineer Braindumps
- Positive XSIAM-Engineer Feedback 😎 XSIAM-Engineer Braindumps 🦪 Reliable XSIAM-Engineer Test Question 🚠 Go to website 「 www.troytecdumps.com 」 open and search for ▛ XSIAM-Engineer ▟ to download for free 😵New XSIAM-Engineer Test Format
- Valid XSIAM-Engineer Exam Simulator 📲 Latest XSIAM-Engineer Guide Files 💌 XSIAM-Engineer Latest Test Report 🤗 The page for free download of ➽ XSIAM-Engineer 🢪 on ( www.pdfvce.com ) will open immediately 🥎XSIAM-Engineer Hot Spot Questions
- XSIAM-Engineer Latest Test Report 🍼 New XSIAM-Engineer Test Format 🟢 Valid XSIAM-Engineer Exam Simulator 🚇 Enter 《 www.dumpsmaterials.com 》 and search for ▛ XSIAM-Engineer ▟ to download for free ➖Valid XSIAM-Engineer Test Book
- Test XSIAM-Engineer Dumps Pdf 🎦 XSIAM-Engineer Reliable Exam Online 🔩 XSIAM-Engineer Reliable Exam Online 🈵 Search for ☀ XSIAM-Engineer ️☀️ and obtain a free download on ➡ www.pdfvce.com ️⬅️ 🕞Exam XSIAM-Engineer Tips
- Pass Guaranteed Quiz 2026 Fantastic XSIAM-Engineer: Palo Alto Networks XSIAM Engineer Exam Outline 🧚 Copy URL 《 www.pass4test.com 》 open and search for [ XSIAM-Engineer ] to download for free 💼XSIAM-Engineer Braindumps
- www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, learn.csisafety.com.au, keithqyma993103.blogofchange.com, bookmarkbooth.com, paidforarticles.in, www.stes.tyc.edu.tw, socialimarketing.com, dawudrucx654432.ziblogs.com, aliviapsyx707707.goabroadblog.com, Disposable vapes
2026 Latest ActualTestsIT XSIAM-Engineer PDF Dumps and XSIAM-Engineer Exam Engine Free Share: https://drive.google.com/open?id=1QqheTC7pUgDn6Cy5FD0Zm_HQM8ux4JyB
Courses
No course yet.